The Most Dangerous AI Agent Won’t Be the Smartest
Everyone is asking how intelligent AI agents will become.
I think we should be asking a different question:
How much power will we give them?
An AI agent can already be designed to:
→ access data
→ call APIs
→ execute code
→ interact with other agents
→ move information
→ make decisions
→ operate without constant human supervision
Intelligence is only one side of the equation.
Permissions are the other.
Give an agent read-only access and a mistake might be annoying.
Give it permission to send money, modify infrastructure, delete data or change security settings…
and suddenly a small mistake can become an enormous event.
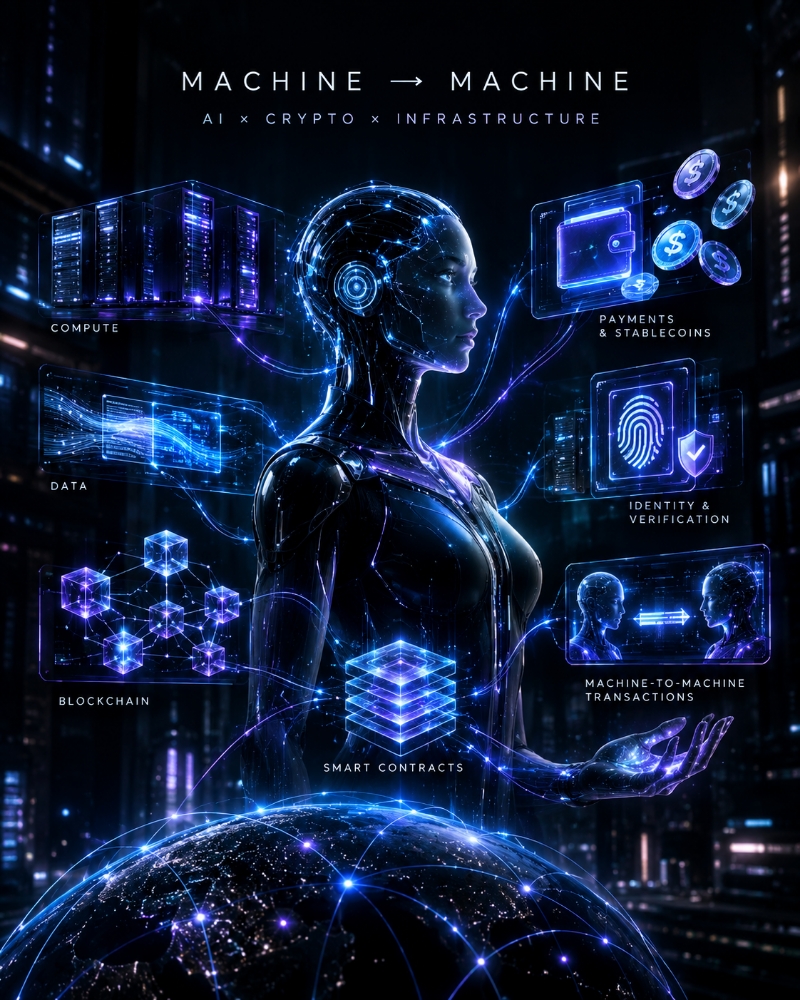
This is why I think the next big layer of AI infrastructure won't just be models.
It will be:
🆔 Agent identity
🔐 Programmable permissions
👁️ Continuous monitoring
⚡ Runtime controls
🧾 Verifiable actions
🛑 Emergency revocation
OWASP is already documenting risks around excessive agency, tool misuse, identity and privilege abuse, memory poisoning and cascading failures in agentic systems.
And the industry is starting to react.
CrowdStrike, for example, introduced an Agentic Identity Provider in September 2026 specifically around giving AI agents trusted identities and controlling their access dynamically.
That tells me something important:
AI security may become an entirely new infrastructure market.
Because eventually we won't just have millions of humans online.
We may have millions of agents.
And every agent will need an identity.
Every identity will need permissions.
Every permission will need boundaries.
And every action may need to be traceable.
The real breakthrough won't be an AI that can do everything.
It will be an AI that can do exactly what it's allowed to do — and nothing more.
Intelligence gives an agent power.
Infrastructure decides how that power is used.
— OrionAria
Would you give an AI agent access to your money if every action was cryptographically limited and reversible? 👀